IN Brief:
- Goodix's new integrated offering combines fingerprint Match-on-Chip processing with an embedded secure element.
- Fingerprint capture, feature extraction, template storage and comparison are performed inside the biometric module, with results passed to the secure element through an encrypted connection.
- The architecture supports FIDO2 and TLS 1.3, but component-level protection does not independently establish the security of a completed connected product.
Goodix Technology has introduced an integrated fingerprint authentication and embedded secure-element offering intended to protect sensitive credentials within connected electronic products. The architecture combines fingerprint Match-on-Chip processing with hardware-based credential storage, separating selected security functions from the host application processor.
Announced on 19 October, the integrated solution forms part of a broader Goodix authentication portfolio that includes Match-on-Host, Match-on-Chip and the combined Match-on-Chip plus embedded secure element, or eSE. The company is targeting devices including industrial and connected terminals, robotics equipment, wearables, intelligent cockpit systems and other products requiring local identity verification.
The three approaches differ principally in where biometric information is processed and which components handle security-sensitive operations. In a Match-on-Host arrangement, the main processing platform participates in biometric operations. Match-on-Chip places fingerprint acquisition, feature extraction, template storage and matching within the fingerprint module itself.
Keeping these functions inside the module reduces the requirement for the host processor to handle raw fingerprint information. It also allows the main processor to receive a match result rather than performing the entire comparison. Goodix identifies this processing arrangement as suitable for connected devices with constrained computing resources or battery capacity.
Fingerprint authentication begins with the acquisition of information about the structure of a user’s fingerprint. The sensing method determines how those characteristics are captured. The resulting information is processed to identify features that can be compared with a previously enrolled reference template.
A fingerprint template is a processed representation of selected biometric characteristics rather than simply a conventional photograph. During authentication, the system compares newly acquired information with the reference and determines whether the result satisfies the configured matching criteria. The resulting decision can be used to authorise an operation, subject to the surrounding security policy.
Goodix says its Match-on-Chip system follows the Secure Device Connection Protocol, or SDCP, and supports unique keys for individual devices. These mechanisms are intended to protect communications between the biometric module and the host, limiting the exposure of sensitive information as it passes between different parts of the electronics system.
Moving biometric processing away from the host changes the distribution of security responsibilities, but does not eliminate attacks against the complete product. The enrolment procedure, physical sensor, firmware, electrical interfaces and application software remain relevant. A biometric match can also be misused if the receiving system accepts an unauthorised or incorrectly authenticated result.
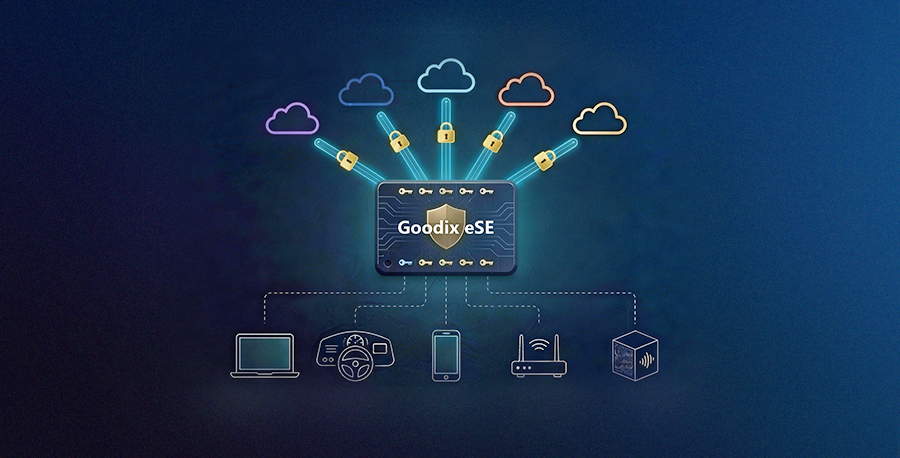
The integrated Match-on-Chip plus eSE architecture adds another hardware security boundary. The secure element contains protected storage and cryptographic functions intended to handle sensitive information separately from the host processor’s ordinary execution environment. Goodix identifies API keys and account login tokens among the credentials that can be managed through this arrangement.
The company says the fingerprint module passes its match result to the secure element using an encrypted connection. The secure element can then evaluate whether a protected operation has received the required biometric authorisation. This separates the comparison of the fingerprint from the component responsible for controlling access to certain credentials.
The design addresses a potential weakness in connected systems where authentication credentials are stored in application memory or files accessible to general-purpose software. If such a host environment is compromised, improperly protected credentials can become available to an attacker. Isolating credentials in dedicated security hardware is intended to reduce the amount of sensitive information accessible through that route.
Goodix’s security offering also supports FIDO2 authentication and TLS 1.3. FIDO2 provides a framework for authentication using cryptographic credentials, while TLS protects communications between endpoints through authenticated key establishment and encryption. The company describes arrangements in which credentials and cryptographic operations can remain within the secure element rather than exposing secret keys to the host.
These functions have different purposes. Biometric matching can help establish that a particular user is present, cryptographic authentication can establish control of an authorised credential, and protected communications can secure information exchanged with another system. A robust product architecture must establish how these elements interact and which operations each component is permitted to perform.
Goodix says the arrangement can manage credentials used for cloud-based AI services and keep selected keys and tokens out of ordinary host memory. It also describes security policy enforcement and tamper-resistant audit logging for operations initiated by software agents. These are supplier-described capabilities whose effectiveness depends on the selected components, firmware configuration and application integration.
The October announcement builds on Goodix’s earlier development of secure elements for AI-agent applications. In April 2026, the company described an eSE architecture intended to isolate cloud-service credentials from host software. The new development adds integrated biometric authorisation to that security approach rather than representing the first introduction of the underlying secure-element technology.
Goodix continues to offer several fingerprint sensing technologies. Capacitive sensors measure electrical characteristics associated with a finger’s surface, while optical sensors use light to obtain fingerprint information. Ultrasonic devices use acoustic sensing and can provide alternatives where enclosure design or the absence of a conventional display affects sensor placement.
Each approach imposes different mechanical and electrical integration requirements. Cover thickness, sensing area, moisture, surface contamination and the positioning of the user’s finger can influence practical operation. These factors must be considered alongside authentication accuracy, response time and energy consumption when selecting a sensing arrangement.
The company has previously announced security certifications for individual secure-element products. Those certificates relate to the evaluated devices and configurations, not automatically to every combined fingerprint and secure-element product. Goodix’s October statement about certified hardware should not be interpreted as a single completed security certification covering all possible sensor, secure-element and host combinations.
Complete-product protection will also depend on firmware updates, credential provisioning, recovery procedures and control of the software requesting protected operations. Separating a key from the host processor can limit one attack path, but it does not determine whether every instruction sent to the security component is appropriate or whether connected services are themselves trustworthy.
Goodix has not identified a universal ordering configuration, initial shipment volume or named customer deployment for the newly integrated offering. The next engineering evidence will concern specific product combinations, the security certification applicable to each configuration and measurements of authentication behaviour when the biometric module, secure element and host processor operate together.